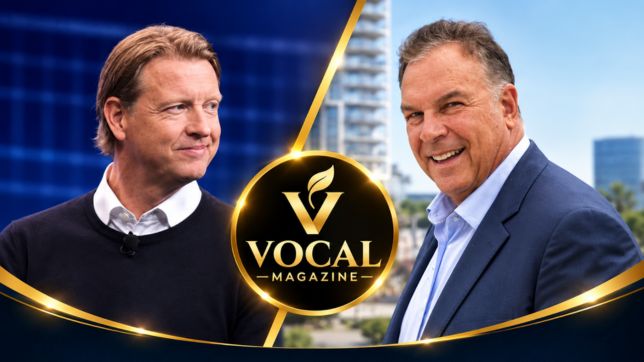
The names Hans Vestberg and Jeff Greene became connected in public discussions surrounding one of the most significant telecommunications cybersecurity incidents in the United States: the campaign widely known as Salt Typhoon. Although Vestberg and Greene occupied very different positions, their roles represented two sides of the same national cybersecurity challenge. Vestberg was the chief executive of Verizon, one of the world’s largest telecommunications companies, while Greene served as a senior cybersecurity official at the Cybersecurity and Infrastructure Security Agency (CISA), the federal agency responsible for helping protect critical infrastructure.
The Salt Typhoon campaign exposed the vulnerability of telecommunications infrastructure to sophisticated cyberespionage. Verizon was among the major telecommunications companies affected, and Vestberg participated in a November 2024 White House meeting with other telecom executives as federal officials sought to coordinate the response. Greene, meanwhile, became one of the most visible government officials explaining the difficulty of determining whether the attackers had been completely removed from compromised networks. Reuters reported that Vestberg and other telecommunications executives attended the November 22 White House meeting, while Greene later told reporters that it was impossible to predict when there would be a “full eviction” of the hackers.
The connection between Hans Vestberg and Jeff Greene therefore provides a useful way to understand the Salt Typhoon incident from both the corporate and government perspectives.
Who Was Hans Vestberg?
Hans Vestberg built a long career in the telecommunications and technology industries before becoming Verizon’s chief executive officer in 2018. He previously served as president and CEO of Ericsson and held several technology and financial positions during his long career with the Swedish telecommunications company.
At Verizon, Vestberg became closely associated with the company’s major investment in 5G infrastructure. Verizon’s own biography describes him as an architect of its 5G network strategy and notes that he served as CEO from 2018 to 2025.
Because Verizon operates critical communications infrastructure used by millions of customers, cybersecurity became an increasingly important part of the company’s responsibilities during Vestberg’s tenure. Telecommunications networks carry enormous quantities of sensitive information, including call records, authentication data, business communications, and other forms of digital traffic.
That made Verizon an important participant in the federal response to Salt Typhoon.
What Was Salt Typhoon?
Salt Typhoon is the name commonly used by cybersecurity researchers and governments for a sophisticated cyberespionage campaign associated by U.S. authorities with Chinese state-sponsored actors. The campaign targeted telecommunications and other infrastructure.
According to CISA, Chinese state-sponsored cyber actors have targeted telecommunications networks and have focused particularly on backbone routers, provider-edge routers, and customer-edge routers. The agency’s 2025 advisory also explained that these actors can modify routers and maintain persistent access, allowing them to move between networks. CISA noted that the activity partially overlaps with what the cybersecurity industry calls Salt Typhoon.
The significance of the campaign was not simply that individual accounts were compromised. Telecommunications infrastructure can provide attackers with visibility into enormous amounts of information. U.S. officials said that the campaign resulted in the theft of call-record information and, in some cases, access to communications involving highly targeted individuals. Reuters reported in December 2024 that officials believed a large number of Americans had their call metadata stolen, while a smaller number of targeted individuals had communications intercepted.
Hans Vestberg and the White House Response
The role of Hans Vestberg became particularly visible in November 2024. As Verizon’s CEO, he joined other telecommunications executives for a White House meeting concerning the growing cyber threat.
The November 22 meeting brought together telecommunications leaders and senior national-security officials as the government worked to understand the scale of the intrusion and coordinate with affected companies. Reporting identified Vestberg, AT&T CEO John Stankey, Lumen CEO Kate Johnson, and representatives of other telecom companies as participants.
For corporate leaders, the incident created an unusually difficult responsibility. Telecommunications companies had to investigate their own networks while simultaneously working with federal agencies investigating a foreign intelligence operation.
Vestberg’s position illustrates how modern CEOs of critical-infrastructure companies are increasingly involved in national-security issues. A telecommunications company’s security decisions can have consequences beyond customers and shareholders because its infrastructure forms part of the country’s communications ecosystem.
The incident also prompted congressional scrutiny. In November 2024, Senator Chuck Grassley wrote to Vestberg seeking information about the Salt Typhoon intrusion and the effect on Verizon’s systems and customers.
Jeff Greene and the Government Investigation
Jeff Greene represented a very different side of the response. As CISA’s executive assistant director for cybersecurity, Greene was involved in explaining the government’s assessment of the incident and the challenges facing investigators.
One of his most widely reported comments came in December 2024. Greene said that, given the stage of the investigation, it was impossible to predict when officials would have achieved a “full eviction” of the hackers from affected networks. The statement illustrated the difficulty of investigating an adversary capable of maintaining persistence inside complex telecommunications infrastructure.
Greene’s comments were significant because they demonstrated that discovering an intrusion is not the same as proving that the attacker has been completely removed.
A sophisticated threat actor may establish multiple access points, compromise credentials, modify network configurations, or exploit legitimate administrative tools. Investigators therefore have to determine not only where the attacker entered but also whether additional persistence mechanisms remain.
CISA subsequently emphasized the importance of improved network visibility, configuration management, vulnerability management, and information sharing across the telecommunications sector.
Why the Salt Typhoon Investigation Was So Difficult
One of the central lessons of Salt Typhoon is that telecommunications networks are extraordinarily complicated.
Large telecom providers operate thousands of pieces of network equipment, data centers, routers, software systems, customer interfaces, and third-party technologies. A threat actor that compromises an important administrative system may potentially gain access to a much wider environment.
Government officials therefore faced a challenge that went beyond identifying a single malicious computer or account. They needed to understand the attacker’s techniques, identify compromised infrastructure, assist private companies with remediation, and determine whether the attacker had established additional footholds.
The campaign also highlighted the importance of public-private cooperation. CISA later explained that its understanding of the broader campaign benefited from collaboration among federal agencies and private-sector partners. Former CISA officials have also emphasized the role of threat hunters and industry information-sharing in identifying the extent of the operation.
Congressional and Industry Scrutiny
Salt Typhoon continued to attract congressional attention after the initial discovery. Lawmakers sought information from telecommunications companies about how the attacks occurred, what data was exposed, and what steps were taken to secure the networks.
In June 2025, Senator Maria Cantwell’s committee requested information from Verizon concerning remaining vulnerabilities associated with Salt Typhoon and asked for documentation supporting the company’s claims that the incident had been contained. The committee noted continuing concerns among security experts about whether the telecommunications sector had taken sufficient steps to prevent similar attacks.
This scrutiny demonstrates a broader issue in critical-infrastructure cybersecurity: determining responsibility for security cannot always be separated cleanly between government and private companies.
Companies own and operate much of the infrastructure, but federal agencies possess intelligence, investigative capabilities, and national-security responsibilities. Effective defense therefore requires both sides to cooperate.
Hans Vestberg’s Departure From Verizon
Hans Vestberg’s later departure from Verizon has sometimes been discussed alongside the company’s experience with Salt Typhoon. However, it is important to distinguish documented facts from speculation.
Verizon announced on October 6, 2025, that Dan Schulman would become CEO immediately, replacing Vestberg. The company said Vestberg would remain as a special adviser through October 4, 2026, and continue as a board member until the 2026 annual meeting. Verizon’s announcement described the change as part of a transition into the company’s next phase and highlighted Vestberg’s contributions to network investment and the company’s strategy.
There is no public evidence in Verizon’s announcement establishing that Salt Typhoon caused Vestberg’s departure. Consequently, it would be inaccurate to present the cyberattack as the documented reason for his removal.
After leaving the CEO role, Vestberg continued working in the technology and business world. In March 2026, Consello announced that he had joined the firm as a Senior Operating Advisor.
His post-Verizon role demonstrates that his career continued beyond the leadership transition at Verizon.
The Broader Significance of Hans Vestberg and Jeff Greene
The connection between Hans Vestberg and Jeff Greene is ultimately less about a direct professional relationship and more about the two different responsibilities represented by their positions during the Salt Typhoon crisis.
Vestberg represented the corporate side of telecommunications infrastructure. His responsibility was connected to operating a huge private network, protecting customers, cooperating with investigators, and maintaining confidence in Verizon’s services.
Greene represented the federal cybersecurity response. His role involved helping government agencies understand the threat, assisting affected organizations, communicating security guidance, and explaining the limits of what investigators knew.
Together, their roles illustrate a central principle of modern cybersecurity: critical infrastructure cannot be protected by government agencies or private companies acting independently.
Lessons From the Salt Typhoon Incident
Several important lessons emerged from the Salt Typhoon campaign.
First, telecommunications networks require continuous security monitoring. Traditional perimeter defenses may not be enough against sophisticated actors capable of compromising legitimate credentials and network equipment.
Second, companies need strong visibility into their network infrastructure. Without comprehensive logging and monitoring, attackers can remain inside systems for extended periods without immediate detection.
Third, public-private information sharing is essential. Government agencies may possess intelligence about an attacker that can help private companies identify previously unknown compromises.
Fourth, cybersecurity needs to be treated as a long-term operational responsibility rather than a one-time technical project. Threat actors continuously develop new techniques, making ongoing investment necessary.
Finally, Salt Typhoon demonstrated that cybersecurity incidents affecting telecommunications companies can become national-security events. The infrastructure operated by private corporations may be essential to government communications, businesses, emergency services, and ordinary consumers.
Conclusion
The story of Hans Vestberg and Jeff Greene provides two contrasting perspectives on the Salt Typhoon cybersecurity crisis. Vestberg, as Verizon’s CEO, represented the telecommunications industry at a critical moment when federal officials and major companies were working to understand a sophisticated intrusion. Greene, as a senior CISA cybersecurity official, represented the government’s effort to investigate the campaign, assist victims, and determine whether attackers had been fully removed.
The Salt Typhoon campaign revealed the extraordinary complexity of protecting modern telecommunications infrastructure. Greene’s warning that a complete “eviction” timeline could not yet be predicted demonstrated the difficulty of establishing certainty during an active investigation. At the same time, Vestberg’s participation in the White House response showed how cybersecurity has become a central responsibility for executives overseeing critical communications networks.
The later transition of Vestberg out of Verizon should be considered separately from the Salt Typhoon investigation because public company statements do not establish that the cyberattack caused his departure. What can be established is that his tenure included major investment in Verizon’s network infrastructure, while Greene’s public role highlighted the continuing challenges of defending that infrastructure against sophisticated state-sponsored cyber threats.
Ultimately, Salt Typhoon was not simply a story about one company, one government agency, or two executives. It was a demonstration of how deeply telecommunications security is connected to national security, corporate responsibility, privacy, and the resilience of modern society.
FAQs
Who are Hans Vestberg and Jeff Greene?
Hans Vestberg is a telecommunications executive who served as Verizon’s CEO from 2018 to 2025. Jeff Greene is a senior U.S. cybersecurity official who has been associated with CISA’s response to major cyber threats, including the Salt Typhoon campaign.
What is Salt Typhoon?
Salt Typhoon is the name commonly used for a sophisticated cyberespionage campaign associated by U.S. authorities with Chinese state-sponsored actors. The campaign targeted telecommunications networks and compromised systems belonging to multiple providers.
How are Hans Vestberg and Jeff Greene connected to Salt Typhoon?
Their connection comes from their different roles in the response to the telecommunications cyberattack. Vestberg represented Verizon during discussions involving major telecom companies and U.S. officials, while Greene publicly discussed the government’s cybersecurity investigation and remediation efforts.
What did Jeff Greene say about removing the hackers?
Greene said that it was impossible to predict when the government would achieve a “full eviction” of the hackers from compromised networks, highlighting the difficulty of determining whether sophisticated attackers had been completely removed.
Was Hans Vestberg’s departure from Verizon caused by Salt Typhoon?
Publicly available Verizon announcements do not establish that Salt Typhoon caused Vestberg’s departure. Verizon announced in October 2025 that Dan Schulman would succeed Vestberg as CEO as the company moved into its next phase.
Why was Salt Typhoon significant for telecommunications companies?
The campaign demonstrated the potential national-security consequences of compromising telecommunications infrastructure. Telecom networks carry sensitive communications and data, making them attractive targets for sophisticated cyberespionage operations.
What cybersecurity lessons came from Salt Typhoon?
The incident highlighted the importance of continuous network monitoring, strong access controls, detailed logging, vulnerability management, threat hunting, and close information sharing between telecommunications companies and government cybersecurity agencies.
Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene Hans Vestberg and Jeff Greene